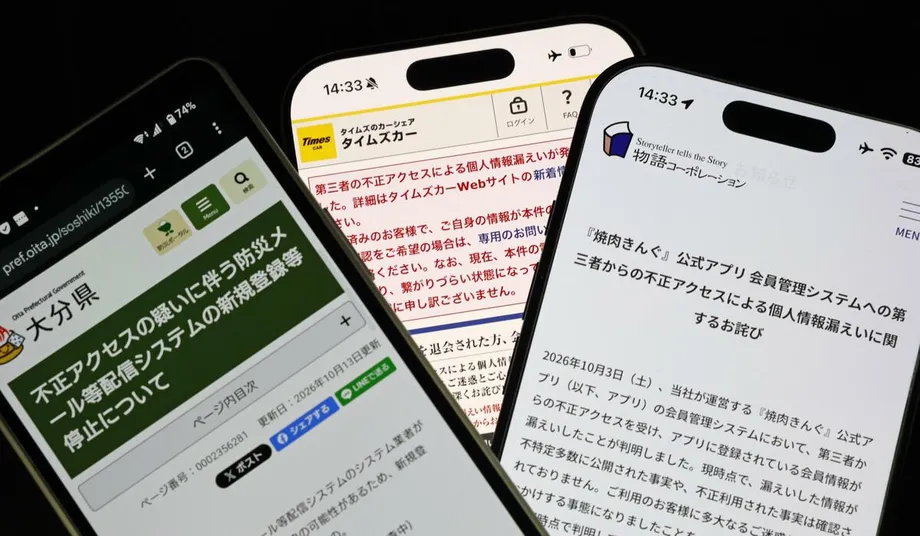
Data Leaks Turn Into Losses for Customers
Japan will draw up an emergency cybersecurity package by the end of the week beginning November 2, Prime Minister Sanae Takaichi said on October 26, 2026, as attacks on companies exposed personal information and left some customers facing losses from unauthorized financial transactions.
Contents
- Data Leaks Turn Into Losses for Customers
- What the Emergency Package Will Cover
- Why So Many Ministries Are Involved
- How the GMO Breach Reached Trading Accounts
- Compensation and Threats Against Users
- What Active Cyber Defense Allows
- Who Decides Whether to Intervene?
- Testing Defenses and Investigating the Attack
- The Dates Behind the Emergency Response
- Key Points
The announcement followed a breach involving GMO Internet Group, which said 26,739 servers were potentially affected, involving trading accounts at more than 70 securities firms, foreign exchange providers and other businesses in Japan and overseas. A customer in Kanagawa Prefecture said unauthorized foreign exchange trades had cost him more than 6 million yen.
Takaichi convened the government's first meeting of relevant ministers on cybersecurity at her office in Tokyo. She called for a coordinated response that could include using new legal powers to enter attackers' systems and neutralize threats, alongside stronger testing and monitoring of Japanese businesses.
Chief Cabinet Secretary Minoru Kihara's October 26 briefing announced the meeting for 6 p.m. and set out the government's central concern: repeated large information leaks were now being followed by further harm through the misuse of stolen data. Ministries would discuss both additional measures and closer cooperation.
Takaichi described the urgency after the meeting, pointing to the damage caused when leaked information is used against the people it belongs to.
"The situation is serious, with growing concerns about civil damages resulting from the misuse of leaked information. We must urgently strengthen our countermeasures," she said.
The immediate task is broader than repairing compromised computers. Ministers must address how stolen information can expose customers' money, how businesses detect intrusions, and when the state should intervene against an attacker.
What the Emergency Package Will Cover
Takaichi identified simulated attacks using generative artificial intelligence and a monitoring network extending to small and medium sized enterprises as measures to strengthen Japan's defenses. Generative AI produces content such as text or computer code; in a controlled security test, it can help create attack scenarios to check how a system responds.
A simulated attack is an authorized exercise. Security teams try to find weak points before criminals exploit them. A monitoring network serves a different purpose: it watches for suspicious activity so organizations can detect and respond to an intrusion.
The proposed reach into smaller businesses matters because the government's response is intended to extend beyond major companies and public bodies. The package would bring more businesses into a coordinated effort to spot attacks and share warnings.
Takaichi instructed ministers to examine the measures and their funding promptly. She also called for the full strength of the government to be brought together to accelerate the work. The package's budget, detailed monitoring arrangements and exact publication date have not been announced.
Why So Many Ministries Are Involved
Kihara's announcement listed participants responsible for cybersecurity, policing, finance, communications, industry, transport and defense. Alongside Takaichi and Kihara, those named included cybersecurity minister Toshiharu Furukawa, National Public Safety Commission chairman Yasuhiro Hanashi and Defense Minister Shinjiro Koizumi.
The range of responsibilities reflects the different parts of the problem. A breach at a server provider can expose information used by financial customers. Police may investigate criminal activity, while defense authorities have responsibilities under the new framework for countering cyber threats.
The October 26 meeting was intended to give ministers a shared picture of current incidents and strengthen cooperation between their departments. It followed proposals delivered to Takaichi on October 23 by the ruling Liberal Democratic Party's cybersecurity strategy headquarters.
The party called for a dedicated response headquarters under the prime minister's office, greater awareness among corporate executives, particularly at listed companies, and stronger recruitment and training of cybersecurity professionals. Takaichi pledged to address cybersecurity under the leadership of her office.
How the GMO Breach Reached Trading Accounts
GMO acknowledged on October 24 that information from Onamae.com Desktop Cloud, a service that rents access to remote servers, may have been taken. Customers use the service for automated foreign exchange trading, allowing trading software to run on a remote computer rather than relying on a computer at home.
Foreign exchange margin trading, usually called FX trading, involves taking positions on changes in currency prices while putting up only part of the value of the trade. Customers can suffer substantial losses when transactions move against them. In this case, customers complained that trades had been made without their permission.
GMO said passwords and other information connected with trading accounts on its servers may have been viewed by third parties. The potential exposure covered 26,739 servers involving accounts at more than 70 businesses. The company has not given a confirmed total for customers who lost money or for the value of their combined losses.
A 44-year-old office worker in Kanagawa Prefecture said unauthorized transactions on October 21 had cost him more than 6 million yen. He described his reaction simply:
"I panicked," he said.
The customer later received an email from a sender identifying itself as "Hacking Team," claiming to have destroyed his account balance. His experience illustrates why the government is treating the misuse of leaked information as an immediate threat to people's finances, as well as a problem for the companies holding their data.
Compensation and Threats Against Users
GMO said it would pay 5,000 yen to every user of the affected service, including those who suffered no financial loss. It also promised compensation for losses it determines resulted from unauthorized access. The general payment and the compensation process therefore address different groups: all service users receive the payment, while trading losses require an assessment.
GMO chief executive Masatoshi Kumagai apologized in a blog post on October 25 for the company's failure to protect customers and pledged compensation. He also asked the government to use active cyber defense measures.
GMO said the suspected attacker had demanded money and threatened to release company and customer information. The company explained why paying would leave customers exposed:
"Even if we were to comply with the demands, there is no guarantee that the acquired information would be deleted or that its misuse would be prevented," GMO said.
On October 24, a person believed to be behind the attack also threatened online to launch ransomware attacks against customers' computers. Ransomware is malicious software that can lock files or systems and demand payment. GMO urged users to back up their data and run virus scans.
What Active Cyber Defense Allows
Japan's Active Cyber Defense Act passed parliament in May 2025 and took effect on October 1, 2026. Its access neutralization provisions allow authorities to enter attackers' systems and take action to stop cyber threats at their source.
The approach moves beyond defending a victim's own computers. Instead of only blocking incoming activity or repairing damage, authorities can act against the systems being used to carry out an attack. Police and the Self-Defense Forces have roles in implementing the framework.
Takaichi said the government would strategically select and carry out available responses, including access neutralization, against cyberattacks whose circumstances had been identified. Her statement placed investigation and operational judgment at the center of any decision.
GMO's request brought those powers into a concrete dispute involving private customers' assets. Kumagai acknowledged that government intervention is typically associated with critical infrastructure operators, such as utilities and transport companies, and recognized that authorities decide when and how to act.
Kumagai argued that attacks using the same methods could spread beyond a private company's services to other infrastructure and personal assets. His appeal sought to make the newly effective law part of the response to losses already being reported by customers.
Who Decides Whether to Intervene?
Kihara said the government would make its own judgment about whether access neutralization was warranted. A company's request can bring information and urgency to authorities, but the decision rests with the state under the relevant legal requirements.
Asked about the response to GMO, Kihara declined to discuss operational details, saying that commenting on individual attacks could reveal government strategy. He described the government's usual approach to information received from affected organizations:
"As a general matter, the government receives various forms of information from affected organizations and provides the necessary support and takes appropriate measures according to the circumstances of each case," he said.
An official at the prime minister's office said further analysis would be needed to determine whether the GMO case qualified. Any operation would likely remain undisclosed because publicizing it could reveal government capabilities. For customers and businesses, the public response may therefore be easier to follow through compensation, service protection and policy announcements than through details of action against attackers.
Testing Defenses and Investigating the Attack
Industry Minister Ryosei Akazawa also announced plans to establish a team of ethical hackers the following month. The cybersecurity specialists will work within the Innovation Platform Agency, affiliated with the Ministry of Economy, Trade and Industry, to identify weaknesses in computer systems.
Ethical hackers test systems with permission so that weaknesses can be repaired. Their work would complement the proposed simulated attack tests and monitoring network: testing seeks out vulnerable points, while monitoring looks for signs that someone is trying to exploit them.
Akazawa's announcement came as some ministry webpages and corporate services were partially suspended as a precaution after vulnerabilities were detected in PHP, a programming language widely used to build websites. The ministry had circulated cybersecurity warnings through about 1,000 industry organizations and associations.
Investigators were also examining the tools associated with the GMO intrusion. GMO Cybersecurity by Ierae, a group subsidiary, said it had traced the attack to an artificial intelligence tool called Artex. A CrowdStrike investigation into Artex attacks in South Korea assessed that those threats most likely originated in China. The origin of the GMO attack remains unconfirmed.
The Dates Behind the Emergency Response
October brought the introduction of new government powers, reports of customer losses and a rapid sequence of political decisions. The main dates show how quickly the issue moved from an incident affecting trading customers to a response involving multiple ministries.
- May 2025: Parliament passed the Active Cyber Defense legislation.
- October 1, 2026: The legal framework took effect, including provisions for access neutralization.
- October 21: The customer in Kanagawa said unauthorized FX transactions caused losses exceeding 6 million yen.
- October 23: The Liberal Democratic Party submitted emergency proposals, including a response headquarters under the prime minister's office.
- October 24: GMO acknowledged the suspected theft of information from Onamae.com Desktop Cloud. A threat against customers' computers also appeared online.
- October 25: Kumagai apologized, pledged compensation and sought government intervention.
- October 26: Takaichi held the ministerial meeting and ordered an emergency package for the following week.
The package is the next public policy milestone. Its practical value for businesses and customers will depend on the measures ministers choose, the funding attached to them and how quickly testing, monitoring and incident response reach the organizations being targeted.
Key Points
- Takaichi wants an emergency cybersecurity package completed during the week beginning November 2, 2026.
- GMO said 26,739 servers were potentially affected, involving trading accounts at more than 70 businesses.
- A customer reported losing more than 6 million yen through unauthorized FX transactions.
- GMO promised 5,000 yen to every affected service user and compensation for losses it attributes to unauthorized access.
- Proposed government measures include attack simulations using generative AI and monitoring that reaches smaller businesses.
- Authorities will independently decide whether to use new powers to enter attackers' systems and neutralize threats.