Malware surge drives a shift to earlier intervention
Singapore plans to introduce a national Protective Domain Name Service in 2027, blocking connections to known malicious domains as it strengthens cyber defence following attacks on all four major telecommunications operators. The measure is part of Singapore’s Cybersecurity Strategy 2026, launched on October 13, 2026, at Singapore International Cyber Week at the Sands Expo and Convention Centre.
Contents
- Malware surge drives a shift to earlier intervention
- Four pillars extend protection beyond essential services
- The telecom attacks show why defence must span organisations
- A national command centre will connect intelligence and response
- How domain blocking will work, and how decisions can be challenged
- AI defence will use existing models with secure integration
- The workforce survey puts judgment alongside technical skill
- Accreditation pilot will test common professional standards
- Partnerships turn shared information into practical readiness
- Key Points
The scale of the challenge is visible in figures attributed to the Cyber Security Agency of Singapore (CSA). Its Singapore Cyber Landscape report recorded 284,300 malware infected computer systems detected in 2025, compared with 117,300 in 2024. That is an increase of 167,000, or about 142 percent. These are detections of infected systems, not a count of individual victims or successful attacks.
Senior Minister K. Shanmugam, who is also Coordinating Minister for National Security and Minister for Home Affairs, set out the intended change in national defence at the launch:
Singapore will seek to act earlier, act at national scale and act at the speed of the threat. This shift is an important part of Singapore’s cybersecurity strategy 2026, which we are launching today.
The third national cybersecurity strategy follows editions launched in 2016 and 2021. Its initiatives are to be introduced over the next five years, combining continuous monitoring of essential infrastructure, protection for businesses and individuals, artificial intelligence capabilities and preparation for risks from quantum computing.
The strategy also connects technology investment with professional standards. A voluntary cybersecurity accreditation pilot is scheduled to begin in the second quarter of 2027, reflecting a judgment that faster tools will still require people who can assess evidence, weigh business risks and decide how to respond.
Four pillars extend protection beyond essential services
The strategy sets out four pillars: defending critical infrastructure, securing the wider cyberspace, strengthening capabilities for AI and quantum technologies, and improving resilience through global partnerships. Two supporting priorities focus on the cybersecurity ecosystem and workforce.
For critical infrastructure, the emphasis is on proactive national defence against sophisticated intrusions. Critical information infrastructure means computer systems needed to deliver essential services, including electricity and telecommunications. Disruption to these systems can affect people and businesses far beyond the organisation that owns them.
The wider cyberspace pillar brings organisations, businesses and individuals into the same national effort. It calls for security to be built into systems from the design stage, stronger governance and wider adoption of basic protective practices. National blocking of malicious domains is one practical expression of that broader approach.
The remaining pillars address technologies and relationships that Singapore cannot manage through infrastructure protection alone. AI introduces new ways to attack and defend systems, while advances in quantum computing could threaten existing encryption. International partnerships are intended to preserve an open, secure and interoperable digital environment while improving Singapore’s ability to withstand attacks.
The two supporting priorities give research, innovation, entrepreneurship, industry partnerships and professional development a place alongside operational defence. The government retains a central role, but the strategy explicitly assigns responsibility to technology providers, researchers, businesses, cybersecurity professionals and individuals.
The telecom attacks show why defence must span organisations
The strategy follows the UNC3886 infrastructure attacks publicly acknowledged in July 2025. Subsequent disclosures identified the affected operators as M1, Simba Telecom, Singtel and StarHub. UNC3886 is described as a state sponsored cyberespionage group capable of maintaining access to networks while avoiding detection.
The response, Operation Cyber Guardian, ran for more than 11 months and involved more than 100 government cyber defenders working with all four operators. Announced in February 2026, it was Singapore’s largest coordinated cyber incident response effort to date.
Shanmugam said the operation demonstrated why government and industry must defend interconnected systems together:
A sophisticated attacker does not see the Government and telcos as separate,” he said. “They look across the system and look for the weak point. Our national defence has to look across the system, too. Government and industry have to work closely together in our response.
The threat extends beyond Singapore. In his address, Shanmugam cited coordinated attacks in Poland against more than 30 renewable energy installations and a combined heat and power plant supplying heat to nearly 500,000 people. He also cited the April 2025 breach disclosed by South Korea’s SK Telecom, which affected nearly 27 million user records.
Those incidents illustrate different forms of exposure: possible disruption of energy services and compromise of telecommunications data. They do not establish that the same attackers or methods were involved. Singapore’s response is to plan for persistent attempts against essential services rather than treat each intrusion as an isolated organisational problem.
A national command centre will connect intelligence and response
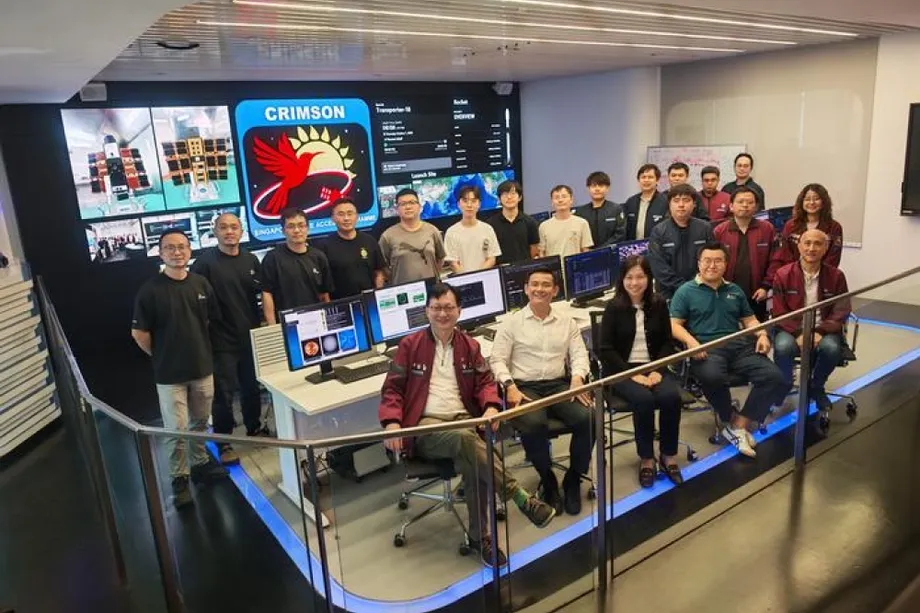
The National Cybersecurity Command Centre (NC3), established in 2025, is CSA’s operations hub for national cyber defence. The strategy develops its role across five areas, linking a national view of threats with monitoring, prevention and coordinated response.
First, NC3 will combine threat intelligence from government agencies, critical infrastructure owners, cybersecurity companies and international partners. Bringing these observations together can help defenders recognise that activity appearing unrelated across separate networks belongs to a larger campaign.
Second, the centre will operate the national Protective Domain Name Service. Third, stronger attack surface management will help infrastructure owners identify systems exposed to the internet and prioritise vulnerabilities that are severe, newly discovered or already being exploited. An attack surface is the collection of systems and access points through which an intruder might enter.
Fourth, selected infrastructure owners will receive privileged threat intelligence and proprietary detection systems developed by the Ministry of Defence’s Centre for Strategic Infocomm Technologies. The centre is working with CSA to deploy those systems and connect their findings with NC3, which will alert defenders to malicious network activity.
Fifth, AI supported operational systems will track incidents, assist assessments and help plan subsequent actions. Together, these functions are intended to shorten the time between detecting suspicious activity and coordinating a national response. They do not remove the need for infrastructure owners to maintain and secure their own systems.
How domain blocking will work, and how decisions can be challenged
A domain name service translates a website address into the network address needed to connect to it. A protective version checks the requested domain against known malicious destinations and can block the connection before a user reaches a phishing page or malware site.
Singapore’s planned service will operate under the Online Criminal Harms Act, which came into force in 2024. The Act permits directions to remove or block access to content suspected of being used for specified criminal activities, including scams and malicious cyber activity.
CSA says blocking decisions will undergo assessment and validation to reduce false positives, meaning legitimate domains incorrectly identified as malicious. Affected individuals and organisations will be able to seek reconsideration and appeal through the Act’s existing processes. These safeguards matter because an incorrect block could prevent access to a legitimate business or service.
A national protective service was recommended in 2022 by Singapore’s Counter Ransomware Task Force as protection before threats reach users. Similar services operate overseas. Trellix executive Neville Vincent cited 11 billion blocked DNS requests across 420,000 domains in Britain in 2022, and more than 67 million malicious domain requests in Australia in 2022–23.
Those figures count requests, not unique people protected or attacks prevented, and cover different periods and services. They indicate potential operating scale rather than predict Singapore’s results. The announced rollout target is 2027; an exact launch date and detailed performance targets have not been specified.
AI defence will use existing models with secure integration
Singapore plans to deploy AI progressively across national cyber defence operations, including NC3 and GovTech’s Government Cyber Security Operations Centre. CSA already has tools that automate discovery and mapping of exposed assets and vulnerabilities and help specialists test complex weaknesses in web applications. GovTech uses AI agents to accelerate vulnerability discovery and security testing.
The government does not intend to build a separate AI model for every task. Instead, it will invest in AI harness engineering, the surrounding software and controls that connect a model securely to tools, data and operational workflows. This approach is intended to let defenders evaluate available models, choose suitable ones and change models when necessary.
Shanmugam described the capability Singapore wants to develop:
What we really need is the capability to evaluate the best available models and to adapt them to our own needs.
The strategy also addresses the risks of the same technology. AI can help attackers find vulnerabilities and operate faster, while agents that take actions through connected tools can be manipulated into accessing information or performing tasks without permission. Shanmugam cited an incident disclosed in Australia the previous month in which an AI agent gained unauthorised access to data on a government portal.
Quantum preparation is a separate part of the technology pillar. Sufficiently advanced quantum computers could defeat some encryption methods used today, creating a need to move toward quantum safe systems. The strategy commits to preparation and migration, but the announcements do not set out a complete national migration schedule.
The workforce survey puts judgment alongside technical skill
The Building Singapore’s Cybersecurity Workforce for the Age of AI report, released on October 13, ranks business judgment as the leading capability needed across professional levels over the next three years. Technical knowledge ranks second, followed by the ability to detect and respond to threats involving AI.
Blackbox Research conducted the CSA commissioned survey between August and September 2026. It covered government agencies, infrastructure owners, cybersecurity service companies and other private organisations using AI. Reports differ in describing the sample as 1,000 organisations or 1,000 practitioners and respondents, so its results should not be treated as a census of every employer or professional in Singapore.
Among respondents, 81 percent said their organisation already used cybersecurity tools with AI functions. Some 92 percent expected to need new skills within the next year, while three quarters worried that some current skills could become less relevant.
For people entering the profession, respondents placed cybersecurity fundamentals first at 65 percent, the ability to verify and challenge AI generated results second at 57 percent, and practical technical experience third at 51 percent. These figures reinforce the report’s conclusion that automation does not make human assessment optional.
Security operations analysts increasingly need to investigate automated findings, judge severity and organise responses rather than simply process alerts. Vulnerability assessment and penetration testing roles also require skills for testing whether AI systems can be manipulated or their safeguards bypassed. Demand for professionals at intermediate and senior levels is expected to rise, while junior roles are expected to include more complex work supported by AI.
Accreditation pilot will test common professional standards
Singapore’s cybersecurity workforce grew from 4,000 in 2016 to more than 10,000 in 2025, an increase of more than 150 percent. The new Cybersecurity Professional Accreditation Framework is intended to give employers a more consistent way to assess that expanding pool of professionals.
CSA is developing a National Cybersecurity Competency Framework with the Infocomm Media Development Authority and SkillsFuture Singapore. It will define knowledge, skills and capabilities across roles and proficiency levels. Accreditation will assess professionals against common standards, taking account of experience, practical ability and professional ethics as well as qualifications.
A separate CSA commissioned study by Ernst & Young in 2024 and 2025 found that professionals struggled to identify skills needed for their roles and career progression. Existing certifications did not comprehensively assess technical knowledge, experience and ethics.
Senior Minister of State for Digital Development and Information Tan Kiat How explained the purpose of the new approach:
“We are not trying to create another layer of certificates. We want to build a framework that gives employers greater confidence, gives professionals greater recognition, and gives the profession a stronger common standard,” said Tan.
By the end of 2026, CSA plans to establish three oversight bodies. A professional office, formed with the Association of Information Security Professionals, will manage assessments, appeals, renewals and a public register. A panel drawn from government, industry and academia will oversee standards and approve titles. Technical committees will review assessment criteria, portfolios and interviews.
The voluntary pilot will run for two years from the second quarter of 2027, initially covering selected government agencies and cybersecurity service providers in security operations, vulnerability assessment and penetration testing. Application fees will be waived. Eligibility, assessment and application details are due from March 2027.
Partnerships turn shared information into practical readiness
The international pillar seeks practical cooperation despite growing competition in AI, semiconductors and telecommunications. At Singapore International Cyber Week, activities included a joint CSA and Google exercise built around an agentic AI cyber scenario, a Frontier AI Governance Workshop for officials from ASEAN and the wider Asia Pacific, and Cloudflare training for critical infrastructure operators.
CSA Chief Executive Gwenda Fong said collaboration must produce an ability to act together:
“For us, cooperation must go beyond agreeing on principles. It must translate into the ability to work together when it matters,” she noted.
The next milestones span operational protection and professional development:
- July 2025: Singapore publicly disclosed the UNC3886 threat to critical infrastructure.
- February 2026: Operation Cyber Guardian was announced after a response lasting more than 11 months.
- October 13, 2026: The third cybersecurity strategy and new workforce initiatives were launched.
- By the end of 2026: CSA plans to establish the three accreditation oversight bodies.
- March 2027: Accreditation eligibility, assessment and application details are due.
- Second quarter of 2027: The voluntary accreditation pilot is scheduled to begin.
- During 2027: The national Protective Domain Name Service is expected to roll out.
The announcements establish direction and several deadlines, but do not provide a complete implementation calendar, a quantum migration deadline or measured outcomes for the proposed domain service. The practical test will be whether national intelligence, blocking, AI tools and professional standards help defenders identify and contain threats earlier.
Key Points
- Detected malware infected systems rose from 117,300 in 2024 to 284,300 in 2025, an increase of about 142 percent.
- A national Protective Domain Name Service is planned for 2027, with validation, reconsideration and appeal procedures.
- NC3 will combine threat intelligence, infrastructure monitoring, detection systems and AI supported response coordination.
- Operation Cyber Guardian involved more than 100 government defenders and all four major telecommunications operators.
- Singapore will invest in secure integration of available AI models and preparation for quantum computing risks.
- A voluntary, fee waived professional accreditation pilot will begin in the second quarter of 2027.