Warnings in 99 countries put Thailand on alert
Thailand's government met Apple on November 11, 2026, after a round of mercenary spyware warnings reached users in 99 countries, including two prominent Thai opposition leaders. The Ministry of Digital Economy and Society planned broader talks with technology and telecommunications companies on November 12, while officials offered device examinations to people concerned about surveillance.
Contents
- Warnings in 99 countries put Thailand on alert
- What Apple's warning tells a recipient
- How spyware can attack without a click
- Opposition leaders seek assurances from the government
- Thailand has a documented surveillance history
- The dates shaping Thailand's response
- How to verify an alert safely
- Where recipients can get a device examined
- Thailand widens checks to banks and communications
- Key Points
Apple sent the latest notifications on October 29. Its warning programme has reached users in more than 150 countries since 2021, a cumulative total covering several rounds of alerts each year. The latest batch involved 99 countries; the larger figure describes the programme's reach over time.
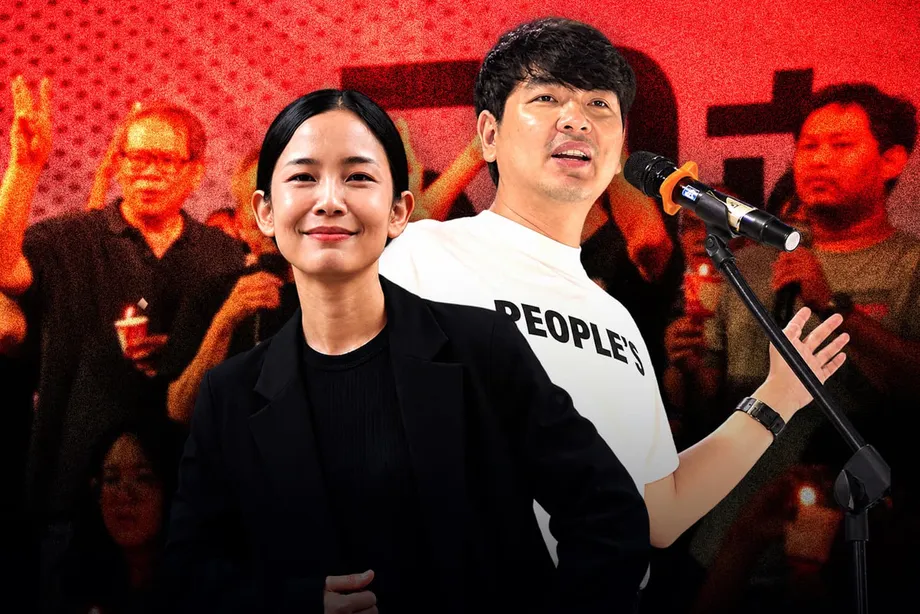
People's Party leader Natthaphong Ruengpanyawut and Democrat Party leader Abhisit Vejjajiva disclosed their warnings on November 3 and raised concerns at Parliament the following day. They sought answers about possible state surveillance as the opposition prepared to question 18 ministers during a confidence debate scheduled for December 7 to 11.
Apple describes these notifications as serious warnings of individual targeting. In its threat notification guidance, published on August 13, 2026, the company says it relies solely on its own threat intelligence and investigations. The warnings concern sophisticated attacks aimed at particular people, often because of their work or public position.
The public record leaves several central questions open: how many people in Thailand received alerts, whether the attempted attacks succeeded, which spyware was involved and who directed the activity. Thai authorities have announced no confirmed harm to users, while a Democrat Party spokesman said Abhisit's phone had not been compromised. Apple was preparing further information and protective advice for Thai users.
What Apple's warning tells a recipient
Apple's system is designed for a narrow group facing unusually expensive and sophisticated surveillance attempts. Journalists, activists, politicians and diplomats are among the people historically targeted by this kind of software. Most Apple users will never face such an attack, the company says.
Apple explains the strength of its assessment in its official guidance:
Although our investigations can never achieve absolute certainty, Apple threat notifications are high-confidence alerts that a user has been individually targeted by a mercenary spyware attack, and should be taken very seriously.
During the Thai discussions, Apple explained that technical metadata had indicated attempted attacks and prompted warnings to potentially affected accounts. Metadata means technical information about activity or communications, rather than necessarily the content of a message.
Digital Economy and Society Minister Chaichanok Chidchob initially encouraged precautions involving public internet connections and trustworthy repair services. Amnesty Tech researchers Rebecca White and Chanathip Tatiyakarunwong challenged that explanation, saying these particular alerts concern advanced targeting rather than ordinary mistakes in everyday internet use.
The practical response is therefore more specific than changing browsing habits. Apple recommends additional device protection and expert assistance for recipients. It keeps the detailed triggers for its alerts confidential because revealing them could help spyware developers change their methods and escape detection.
How spyware can attack without a click
Mercenary spyware is surveillance technology developed commercially for targeted intrusion. Apple says attacks can cost millions of dollars and use tools with a short useful life, because developers need new methods once weaknesses are discovered and repaired.
A zero-click attack can exploit a device without its owner opening a link, downloading a file or taking another action. Attackers use a weakness in software that processes incoming information, allowing an intrusion attempt to begin without the familiar trap of persuading someone to click.
Apple's guidance describes a history of exceptionally costly attacks associated with state actors, including private companies developing spyware on their behalf. It names Pegasus, made by NSO Group, as an example. Apple does not assign its notifications to particular attackers or geographic regions.
Thai officials said the software behind the latest warnings had not been identified. The minister explained that references to Pegasus helped communicate the severity and nature of the threat. Citizen Lab director Ronald Deibert also pointed to a broader commercial market: his research organisation has identified spyware abuse involving around 12 companies.
That market includes tools beyond Pegasus. Citizen Lab separately investigated Paragon's Graphite spyware involving journalists' Apple devices in 2025. The Thai response therefore involves examining technical evidence before selecting a particular product as the focus of an investigation.
Opposition leaders seek assurances from the government
Natthaphong and Abhisit brought the issue into Parliament on November 4, asking whether government or security agencies had targeted their phones. Natthaphong questioned whether people in power were using mechanisms under their control to obstruct or intimidate the opposition. Abhisit called for assurances against unlawful surveillance and violations of personal rights.
Defence Ministry spokesman Surasant Kongsiri said security agencies do not use spyware and have no need to acquire it. He said obtaining politicians' secrets or breaking into their data was outside the military's duties.
Government spokesman Ekkapob Pianpises also denied state involvement. He said no budget had been allocated to procure Pegasus in either the current or previous financial year.
The warnings arrived as opposition parties pursued a motion to question 18 ministers from December 7 to 11. White, a researcher and adviser on surveillance technology and human rights at Amnesty Tech, said the timing was probably coincidental. Apple sends warnings in batches when it detects threats, rather than following a fixed annual timetable.
White pointed to an earlier batch in August that reached users in nearly 100 countries. Deibert, who directs Citizen Lab at the University of Toronto, also described recipients in several countries during the latest round, including a German minister and members of German civil society.
Thailand has a documented surveillance history
Citizen Lab previously documented at least 30 forensically confirmed Pegasus infections in Thailand between October 2020 and November 2021. The research involved iLaw and DigitalReach, and Amnesty International's Security Lab independently checked a sample of those earlier cases.
The earlier infections affected people associated with Thailand's democracy movement. That history helps explain why the opposition leaders are asking for an investigation and why preserving technical evidence matters to the current response.
Digital forensics is the examination of records and traces left on a device. Researchers can look for signs of malicious software, suspicious connections and possible data transfers. Establishing when activity occurred requires that closer examination, Deibert said.
For a politician, journalist or activist, the stakes extend to people who communicate with them. A phone may contain confidential contacts, discussions about investigations and plans for parliamentary scrutiny. Protecting those communications is an immediate practical concern while specialists examine the device.
The dates shaping Thailand's response
Thailand's response developed across several weeks, from Apple's international warning batch to public disclosures by opposition leaders and government discussions about national preparedness.
- October 29, 2026: Apple sent threat notifications to targeted users in 99 countries.
- November 3: Natthaphong and Abhisit disclosed that they had received warnings.
- November 4: The opposition leaders raised their concerns at Parliament, while the Defence Ministry denied that security agencies used spyware.
- November 10: Chaichanok announced plans for talks with Apple and said a clearer national response plan was expected the following week.
- November 11: The ministry and the National Cyber Security Agency discussed the alerts with Apple.
- November 12: Officials planned wider discussions with platform, software, hardware and telecommunications companies.
- December 7 to 11: The opposition's debate concerning 18 ministers was scheduled to take place.
Prime Minister Anutin Charnvirakul had instructed the ministry and relevant agencies to assess escalating global cyberthreats and prepare response measures after discussions at the National Security Council.
The ministry also planned to consult Google about potential threats to Android users. The November 11 meeting focused on Apple; the wider discussions were intended to bring other operating systems, technology suppliers and network operators into the response.
How to verify an alert safely
Apple delivers threat notifications through an alert on the iPhone Lock Screen and in Settings, as well as email sent to addresses associated with the user's Apple Account. A banner also appears at the top of the Apple Account page after sign-in. Notification types can vary with the device model and software version.
Recipients can verify a warning by navigating independently to account.apple.com and signing in. A genuine notification will be visible at the top of the account page. This gives users a way to check an alarming message without following a link inside it.
Apple's official guidance sets out a firm rule for recognising requests that should cause concern:
Apple threat notifications never ask the user to click any links, open files, install apps or profiles, or provide an Apple Account password or verification code by email or on the phone.
Thailand's National Cyber Security Agency issued a similar warning about fake alerts seeking clicks, app installations, passwords or account verification codes. Public concern about a real security incident can create an opportunity for criminals to impersonate a trusted company.
For a genuine alert, Apple recommends enabling Lockdown Mode and seeking specialist support. Lockdown Mode adds restrictions to selected device functions to reduce opportunities for highly sophisticated attacks. Apple also advises people who have good reason to believe they face individual targeting to consider enabling it even without a notification.
Where recipients can get a device examined
Thailand's National Cyber Security Agency said concerned recipients could contact ThaiCERT to coordinate a device examination or seek help from trusted external specialists. Its tools can examine suspicious software, system logs and connections that may be linked to an attacker.
Investigators can look for contact with command and control servers, often shortened to C2. These are systems attackers use to send instructions to compromised devices or receive information from them. Specialists can also examine the internet addresses a phone contacted and traces suggesting information left the device.
The scope and findings of an examination depend on the records and evidence still present. Deibert advised recipients to preserve their devices and avoid wiping them before expert examination, so investigators retain the best chance of finding useful traces.
Apple recommends Access Now's Digital Security Helpline, which offers emergency assistance 24 hours a day, seven days a week. External organisations can provide advice tailored to an individual's situation, while Apple retains the information behind its decision to issue a particular warning.
People seeking ordinary device support can also approach an Apple Store. For suspected spyware targeting, the specialist routes offered by ThaiCERT, trusted forensic examiners and the Digital Security Helpline provide access to more focused security assistance.
Thailand widens checks to banks and communications
The government response extends beyond individual iPhones. Chaichanok said officials were examining risks to banking, health information and the communications systems on which the public relies.
Thailand's banking sector had worked with the National Cyber Security Agency and had so far fended off the threats under review, the minister said. An initial review concerning attacks overseas also found no indication that Thai health information related to blood had been affected. Officials said monitoring would continue.
Deputy Digital Economy and Society Minister Nan Boonthida Somchai said communications infrastructure needed the highest of four emergency readiness levels described in National Security Council guidance. Preparations covered local incidents as well as emergencies occurring simultaneously across the country.
Telecommunications operators were expected to provide readiness updates during the week of the Apple meeting. Although operators already had legal duties to prepare for emergencies and disasters, the ministry wanted those plans updated for changing cyberthreats.
Nan said agencies and private system owners needed to check firewalls and other security tools and report irregularities promptly to the National Cyber Security Agency. Network oversight has technical limits: normal traffic and traffic carrying hidden malicious software can travel through the same communications systems.
For everyday users, Apple's guidance remains practical: install current software updates, use a device passcode or biometric protection, enable two-factor authentication and Stolen Device Protection, and use strong, unique passwords or passkeys. The company also recommends installing apps from the App Store and avoiding links or attachments from unknown senders.
Key Points
- Apple's October 29 warning batch reached users in 99 countries; its notification programme has reached more than 150 countries since 2021.
- Thai opposition leaders Natthaphong Ruengpanyawut and Abhisit Vejjajiva disclosed alerts and sought answers about possible surveillance.
- Apple describes its warnings as assessments made with high confidence that an individual was targeted by mercenary spyware.
- Thai government and defence spokesmen denied state involvement.
- Thailand met Apple on November 11, 2026, and planned broader industry discussions for November 12.
- Recipients can verify alerts through their Apple Account, enable Lockdown Mode and seek expert help.
- ThaiCERT can coordinate device checks; preserving the phone before examination helps retain evidence.
- Thailand is also reviewing readiness across telecommunications, banking and other digital systems.