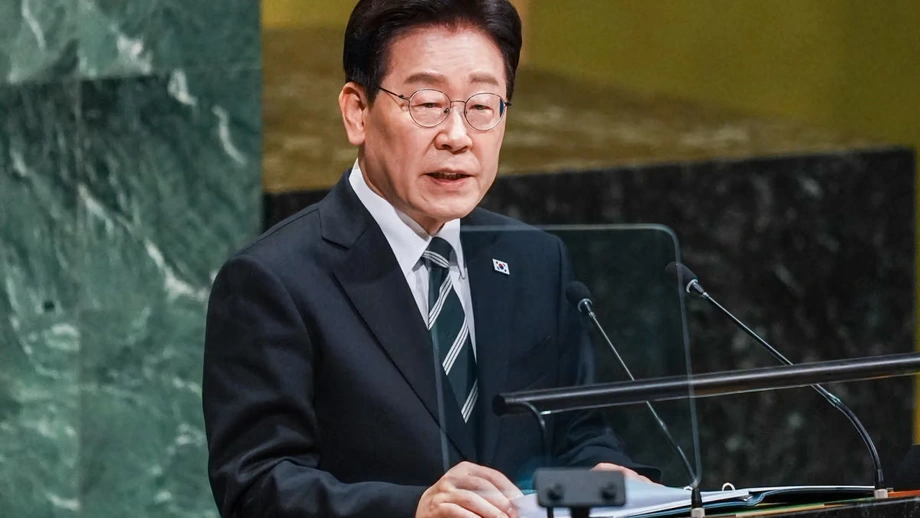
Lee Seeks One Authority to Coordinate Cyber Defenses
South Korean President Lee Jae Myung has ordered officials to examine creating a powerful cybersecurity authority after a reported $6.3 billion theft from Binance, as security checks cover more than 2,100 public institutions and roughly 170 major private infrastructure facilities.
Contents
- Lee Seeks One Authority to Coordinate Cyber Defenses
- Why the Binance Theft Became a Warning
- How the Events Unfolded
- What Would Change Under a Cybersecurity Czar?
- Inspections Reach Public Bodies and Essential Networks
- Korean Breaches Put Customer Information in Focus
- Why Online and Offline Wallets Matter
- Lee Links AI Progress With Stronger Protection
- Key Points
At a Cabinet meeting in Seoul on November 3, Lee called for stronger coordination across government ministries and private companies. His proposal follows attacks involving Korean financial businesses and growing concern about the safety of finance, energy and communications networks.
Lee, who wants officials to detect danger earlier and share warnings faster, described the weakness of the current approach:
The existing security system, which centers on inspections and after-the-fact responses, is showing clear limitations.
The proposed cybersecurity czar would oversee work currently divided among several authorities. A czar in this context means an official or organization with strong powers to coordinate a particular policy area. Lee also asked officials to consider a task force bringing government and private businesses together.
The proposal remains under review. The government has not announced its structure, the powers it would receive from existing agencies or a timetable for establishing it.
Why the Binance Theft Became a Warning
Attackers reportedly withdrew about $6.3 billion in digital assets from Binance on October 29. The theft affected online wallets across ten blockchains, with most of the money taken in about 20 minutes. Blockchains are digital records used to track cryptocurrency transactions.
The speed and spread of the withdrawals help explain Lee's focus on early warnings. An attack unfolding across several networks within minutes leaves little time for institutions to identify suspicious activity, contact the right authorities and limit further losses.
Blockchain analysis company TRM described the incident as the largest cryptocurrency theft on record. The reported $6.3 billion loss was about 4.2 times the $1.5 billion stolen from Bybit in February 2025, illustrating the scale of the incident cited in the policy debate.
The FBI attributed the attack to North Korea on October 31, identifying the TraderTraitor hacking group. North Korea denied responsibility. Kim Yo Jong, the sister of North Korean leader Kim Jong Un, rejected the accusation:
absurd rhetoric and nothing new.
Lee referred to the Binance incident when discussing the need for stronger defenses, but did not name North Korea in his remarks. His instructions focused on how South Korea should organize its response to cyber threats across public services and businesses.
How the Events Unfolded
The theft, the US attribution and Lee's instructions came within several days of one another. Domestic breaches added urgency to a discussion that extended beyond cryptocurrency exchanges.
- February 2025: Bybit suffered a cryptocurrency theft valued at about $1.5 billion, the comparison used to describe the scale of the Binance incident.
- October 29: Attackers reportedly withdrew about $6.3 billion from Binance wallets across ten blockchains.
- October 31: The FBI attributed the Binance attack to North Korea.
- November 3: Lee directed officials at a Cabinet meeting to review a cybersecurity authority and stronger prevention measures.
South Korean authorities were also conducting security reviews across public institutions and major private facilities. The checks provide an immediate response while officials examine a longer term change to how cybersecurity responsibilities are organized.
What Would Change Under a Cybersecurity Czar?
Lee's proposal addresses a practical problem: security responsibilities are spread across institutions with different duties. The National Intelligence Service, the science ministry and financial regulators are already involved in separate parts of the response.
A coordinating authority would bring those functions into a common framework spanning government and private companies. Lee called for a system able to detect signs of attacks, distribute that information and organize a response before the damage grows.
A warning discovered by one organization can matter to another. For example, information about an attempted intrusion may help other institutions check whether they face similar activity. Faster sharing is central to the prevention system Lee described.
The proposed public and private task force would connect government coordination with the businesses operating financial services and other essential networks. Its membership and responsibilities would depend on decisions officials have yet to make.
Inspections Reach Public Bodies and Essential Networks
The National Intelligence Service has ordered emergency security checks at more than 2,100 ministries, local governments and public institutions. The science ministry is reviewing roughly 170 major private infrastructure facilities, including financial and telecommunications operators.
Lee identified finance, energy, and information and communications as priority areas. He instructed officials to address weaknesses at major state institutions and infrastructure, connecting cybersecurity with services people depend on in daily life.
Financial networks support payments and access to money. Communications networks carry information between people, companies and public bodies. Energy infrastructure supports electricity and other essential supplies. Lee's instructions place the protection of these services alongside the protection of digital assets and personal information.
The inspections remain part of the immediate response. The broader reform would add stronger coordination and earlier action, so that authorities can respond to warning signs as well as investigate incidents after they happen.
Korean Breaches Put Customer Information in Focus
Mirae Asset Global Investments, cryptocurrency exchange Bithumb and Daishin Securities have recently been affected by hacking incidents involving customer information. Those cases put the handling of personal data alongside the theft of cryptocurrency in the government's discussion.
Money and information present different problems for affected customers. An exchange may need to replace stolen assets, while a business facing a data breach must address the exposure of information held about its users. Lee's proposed framework covers security across institutions rather than focusing on a single type of loss.
The debate also followed a reported leak of a passenger list for the aircraft used by the president. That incident extended concern beyond financial companies to information connected with state operations.
The Financial Services Commission has summoned representatives of five cryptocurrency exchanges to assess their readiness: Upbit, Bithumb, Coinone, DigitalX and Gopax. The meetings bring domestic trading platforms into the response to the Binance incident and recent Korean breaches.
Why Online and Offline Wallets Matter
Korean exchanges must keep at least 80% of customer cryptocurrency in cold wallets. These wallets keep the digital credentials needed to authorize transfers offline, reducing their exposure to attacks through internet connections.
Hot wallets remain connected to the internet and allow exchanges to process transfers more readily. The reported Binance theft involved hot wallets, making the division between online access and offline storage central to understanding how exchanges manage security.
The Korean requirement means at least four fifths of customer cryptocurrency must be held in cold storage. Up to one fifth may be held outside that minimum allocation. The figures describe a storage requirement; exchange operators still need controls governing access, transfer approvals and the movement of assets between wallets.
Customers also depend on how an exchange responds after a loss. Binance said it had restored services and covered losses from the incident, funding about 95% of the stolen amount from its own reserves. Applied to the reported $6.3 billion theft, that share would equal approximately $5.99 billion.
South Korea's proposed Digital Asset Basic Act would address compensation for customers after hacks, but it has not passed. Compensation is therefore a separate policy issue from the existing requirement to keep most customer assets offline. One concerns how assets are stored; the other concerns who must pay when customers suffer losses.
Lee Links AI Progress With Stronger Protection
Lee warned that advances in artificial intelligence are making hacking methods more sophisticated and more widespread. He argued that security systems need to identify weaknesses and react to early signs of an attack as those methods develop.
Artificial intelligence was part of his explanation for the changing threat environment. His instructions called for prevention measures across technology, government institutions and public awareness, rather than relying on inspections alone.
Lee also tied cybersecurity to South Korea's ambitions in semiconductors and AI. The president said digital competitiveness requires strong protection alongside progress in those industries:
To become a leader in the digital age, we must possess world-class cybersecurity capabilities along with semiconductors and AI.
For public agencies and companies, the immediate work is checking vulnerabilities and preparing to share warnings more quickly. The larger decision is how much authority a new coordinating body would hold over institutions that already have security responsibilities.
For customers, the most concrete issues are the safety of personal information, continued access to financial services and compensation after theft. The proposed cybersecurity authority and the pending digital asset legislation address different parts of those concerns.
Key Points
- Lee has ordered a review of a cybersecurity authority coordinating government agencies and private businesses.
- The proposal follows a reported $6.3 billion Binance theft on October 29 and recent breaches at Korean financial firms.
- The FBI attributed the Binance attack to North Korea, which denied responsibility.
- Security checks cover more than 2,100 public institutions and roughly 170 major private infrastructure facilities.
- Korean exchanges must keep at least 80% of customer cryptocurrency in cold wallets.
- The Digital Asset Basic Act remains unpassed, and no timetable has been announced for the proposed cybersecurity body.