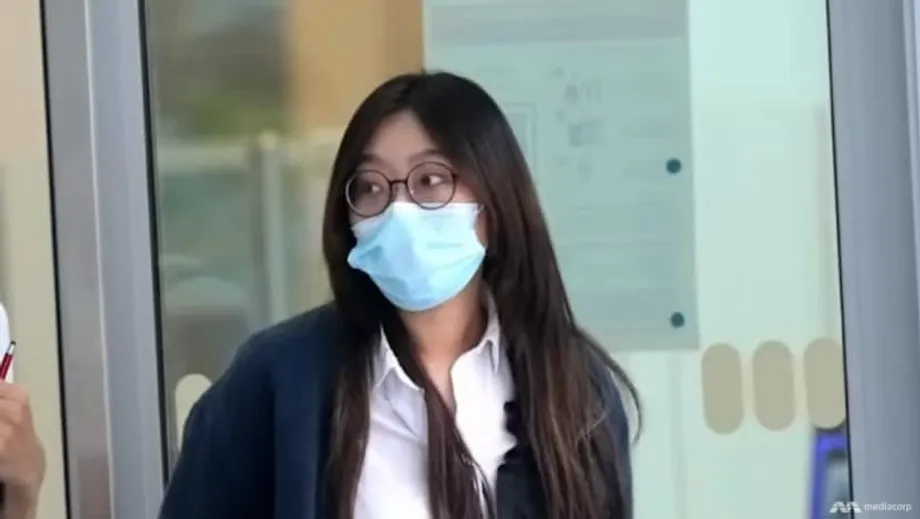
27 charges over customer data sent to a fake police officer
Cao Wenqing, a former junior officer at United Overseas Bank, has been convicted of 14 charges under the Computer Misuse Act and 13 under the Banking Act after disclosing the personal details of more than 1,000 customers to someone pretending to be a Chinese police officer.
Contents
- 27 charges over customer data sent to a fake police officer
- How customer records became a spreadsheet
- When Cao discovered the deception
- Why the callers' threats worked
- Why the court rejected her defence
- What UOB did for affected customers
- Why names and balances are valuable to scammers
- Why misuse by employees is hard to prevent
- Impersonation scams reach customers as well as staff
- Practical steps to protect information and money
- What the conviction means for bank safeguards
- Key Points
The 30-year-old Chinese national, who is a Singapore permanent resident, was found guilty in October 2025. Her sentencing is scheduled for December. The case began in March 2021, when scammers contacted her and claimed she was implicated in an investigation.
Cao used her legitimate work login to search confidential bank records, copied selected information into a spreadsheet and sent photographs of it through WhatsApp. The recipient claimed to be a Shanghai police captain. Investigators later found that she had accessed more than 3,000 customer profiles and transmitted information about well over 1,000 customers.
The court rejected her argument that she believed she was under investigation and felt compelled to cooperate. It found that she understood the confidentiality rules, had received relevant training and failed to check the callers' identities until after the information had been disclosed.
For UOB customers, the exposure involved names, identification numbers, mobile numbers and bank balances. UOB said account numbers were not disclosed and its systems remained secure. The incident nevertheless placed sensitive information in the hands of people who could use it to make fraudulent approaches sound convincing.
The case brings together two kinds of risk: the misuse of access granted to a bank employee and a scam built around fear of official authority. Cao could enter the database for her job, but the court found that she used that access for purposes outside her work and disclosed information she was required to protect.
How customer records became a spreadsheet
Cao worked in UOB's mortgage department, where she could access a bank database strictly for work. The database contained customer names, nationalities, addresses, identification numbers, account numbers and balances.
Two people approached her by telephone in March 2021, introduced themselves as Chinese police officers and warned that she was implicated in a case. Following their instructions, she searched for customers with common Chinese surnames and filtered the results for Chinese nationals.
Cao copied customer names, identification numbers, mobile numbers and balances into an Excel file. She photographed the spreadsheet and sent the images through WhatsApp. When asked to look up particular customers, she also searched for them and sent screenshots of their profiles.
The process matters because the information was obtained through an employee's permitted access to the system. A login allowed Cao to do her mortgage work; it did not give her permission to search records for callers or send confidential customer information outside the bank.
The database held more types of information than those identified as disclosed. UOB's statement that account numbers were not shared is therefore an important detail about the exposure. Names, identification numbers, mobile numbers and balances still gave the recipients sensitive information about individual customers.
When Cao discovered the deception
Cao concluded in April 2021 that she had been deceived after reading about a similar scam and contacting the Shanghai police herself. She made a report to the Singapore Police Force on the same day she was arrested.
The events unfolded over more than four years, from the initial approach to the conviction:
- March 2021: Two callers claiming to be Chinese police officers contacted Cao, who subsequently searched customer records and sent information at their direction.
- April 2021: Cao read about a similar scam, contacted the Shanghai police and concluded that the callers had deceived her. She reported the matter to Singapore police on the day of her arrest.
- October 2025: Cao was convicted of 14 Computer Misuse Act charges and 13 Banking Act charges.
- December 2025: Sentencing is scheduled.
The prison term or fine Cao will receive has not yet been decided. The charges carry penalties that can include fines and imprisonment, depending on the offence.
Why the callers' threats worked
The callers used authority, urgency and fear to pressure Cao into following their instructions. Investigators said she feared inquiries by the supposed Chinese police and did not want to lose her job or be sent back to China.
Government officer impersonation scams commonly begin with a claim that a person is under investigation. The caller then demands cooperation, often in secret. Instructions may include sharing personal information or transferring money, presented as steps that must be taken immediately.
Persistent demands and threats of legal action can make a victim focus on avoiding punishment instead of checking whether the caller is genuine. Requests to communicate only through particular apps can also make a fraudulent exchange feel like an official procedure.
Cao's case shows how those tactics can reach beyond the person receiving the call. Because she worked at a bank, her response exposed information belonging to many other people. The scammers turned pressure on one employee into access to customer data.
Independent verification is the central safeguard against this type of approach. A person can end the call, obtain the agency's telephone number from an official channel and ask whether the claimed investigation exists. Cao eventually contacted the Shanghai police herself, but did so after sending customer information.
Why the court rejected her defence
The court found that Cao knew customer information was confidential and that her database access was limited to work. She had received training on banking secrecy and data handling.
The judge considered her failure to verify the callers' identities unreasonable. Her later decision to contact the Shanghai police after reading about similar scams showed that she was able to make that check.
The court also pointed to her knowledge that her actions breached internal bank policy and Singapore law. That knowledge undermined her claim that she had acted under pressure in good faith. She was convicted on all 27 charges described in the case.
The Computer Misuse Act makes unauthorised access to computer material a criminal offence. In this context, having a working login did not mean every use of the database was allowed. Access granted for bank duties was used to obtain information for people outside the bank.
The Banking Act separately restricts the disclosure of customer information by bank staff and service providers. Disclosure is permitted only in tightly defined circumstances. Those confidentiality duties protect customers whose personal and financial records must be available to employees carrying out legitimate banking work.
What UOB did for affected customers
UOB said it worked with the Singapore Police Force and other agencies after discovering the leak. It contacted all affected customers, disabled their internet and mobile banking access, and helped them reset their digital credentials.
The bank also increased monitoring, added SMS alerts for online transfers of low value and posted warnings about ongoing scams at login. Disabling digital access and resetting credentials were containment measures intended to protect customers while the bank responded to the exposure.
UOB apologised and said customer security remained a top priority. It said its systems were secure, that customer account numbers were not part of the disclosure and that it was cooperating with law enforcement and relevant authorities.
The bank set out its immediate response and customer guidance in its official statement. It advised customers to remain vigilant and report suspicious activity immediately.
The absence of account numbers reduced the risk of direct unauthorised withdrawals. The disclosed personal details still left customers vulnerable to phishing, calls using false caller identities and other attempts to persuade them to reveal information or take actions that would put their accounts at risk.
Why names and balances are valuable to scammers
A customer approached by someone who knows their name, identification number, mobile number and bank balance may find the caller more credible. Those details can help criminals build a persuasive story about a bank account or an investigation.
Social engineering means manipulating a person into doing something that helps an attacker, such as revealing a password or approving a transfer. Rather than breaking through a bank's technical security, the scammer tries to persuade someone with legitimate access to act on their behalf.
The exposed information can be used to mount convincing scams, trick customers in ways that lead to account takeovers or be combined with other leaked data to commit fraud. Phishing is one form of this deception, using messages or other approaches that appear trustworthy to obtain sensitive information.
Customers therefore face a risk that extends beyond the initial disclosure. A later call or message may use accurate personal details to make a false request seem genuine. UOB's advice to report suspicious activity promptly addressed that continuing danger.
Why misuse by employees is hard to prevent
Banks use several layers of protection against outside intrusions and internal misuse. Access controls determine who can see information, audit logs record activity, and monitoring tools can flag unusual behaviour.
Employees nevertheless need access to sensitive records to serve customers. An employee who breaks the rules, or is manipulated into doing so, may perform searches that resemble ordinary work. The difficulty is identifying when otherwise legitimate access is being used for an improper purpose.
Cao's use of photographs also illustrates a practical weakness. Content filters and restrictions on exporting large amounts of data may limit some methods of disclosure, while a personal phone can still be used to photograph information displayed on a screen.
Possible safeguards include granting permissions for limited periods, restricting which staff can search particular fields, adding watermarks, controlling screen capture and limiting personal device use in sensitive work areas. These measures address different parts of the process through which information can leave a bank.
Alerts generated as activity happens can flag unusual search patterns. Examples include looking up thousands of unrelated records across multiple branches or filtering customers by nationality without a documented work purpose. Such checks can help security teams distinguish necessary customer service from searches requiring investigation.
Training and workplace culture are also part of the response. Employees need to recognise impersonation tactics, pause to verify suspicious requests and raise concerns with supervisors or security teams. Clear reporting channels for coercion or suspicious calls can make it easier to seek help before customer information is exposed.
Impersonation scams reach customers as well as staff
Government officer impersonation scams have become one of the most costly forms of fraud in Singapore. Scammers may claim to represent Singapore police or a foreign law enforcement agency, use fake documents or warrant cards, and appear against backdrops resembling official settings.
Their demands can include moving money for an investigation, sharing banking information, sending one time passwords or installing software that allows someone else to control a device remotely. Official sounding calls and threats can persuade victims to comply.
Public advisories say legitimate officers do not request banking credentials, one time passwords or money transfers over the telephone or through messaging apps. They also do not direct people to click links to banking websites.
Demands for secrecy, requests for remote access to devices and instructions to move savings into purported safe accounts are warning signs. Someone uncertain about a call can hang up and contact the bank or agency through its official hotline.
Practical steps to protect information and money
Singapore has invested in education about scams and tools to help people screen calls and messages. Banks have added transaction alerts, waiting periods before new payees can be used and kill switch features that let customers suspend digital access quickly when they suspect a compromise.
These measures reduce risk while criminal groups continue adapting their tactics and targeting both customers and employees. People can combine those protections with straightforward checks when an unexpected caller asks for information or action:
- Verify claims of authority independently. End the call and contact the police agency or bank through an official number, rather than a number supplied in the suspicious message.
- Protect credentials. Do not share banking details, Singpass credentials, card numbers or one time passwords through telephone calls or messaging apps.
- Recognise pressure. Requests for secrecy, rushed decisions or transfers to a purported safe account are strong warning signs.
- Use bank alerts. Enable SMS alerts for transfers of low value and changes to your profile, set transaction limits and check statements regularly.
- Secure devices. Install updates, use official app stores and avoid installing remote access tools unless directed by a trusted technician whom you contacted independently.
- Report quickly. Contact the bank immediately and make a police report if information or accounts may have been compromised. Fast action can help block or recover funds.
A caller's knowledge of personal information can make a demand feel convincing. Checking the request through an independent official channel gives the person receiving it a way to establish who is actually asking.
What the conviction means for bank safeguards
Financial institutions in Singapore operate under confidentiality and technology risk requirements. The Banking Act protects customer information, while the Monetary Authority of Singapore sets detailed expectations for managing technology risks.
Those expectations include control over access permissions, monitoring of activity, response to incidents and security training. Cases involving misuse by employees typically prompt reviews of data access rules, monitoring thresholds and staff handling procedures.
The UOB case shows how fear and coercion can override training and put many customers at risk through one employee's actions. Stronger checks on large numbers of searches, a workplace culture that supports verification and the ability to respond quickly can make it harder for scammers to obtain information through staff.
The response after a disclosure matters too. Prompt containment, direct contact with affected customers and transparency about protective measures can help rebuild trust. UOB's reported actions addressed digital access and monitoring while customers were advised to watch for further attempts at deception.
For Cao, the next step is sentencing in December. For banks and customers, the central lesson of the case is concrete: access to accurate personal information can be exploited by impersonators, and requests made under claimed official authority need independent verification.
Key Points
- Cao Wenqing, a former UOB junior officer, was convicted in October 2025 of 14 Computer Misuse Act charges and 13 Banking Act charges.
- Investigators found that she accessed more than 3,000 customer profiles and transmitted details of well over 1,000 customers.
- She sent photographs of a spreadsheet and customer screenshots through WhatsApp to someone claiming to be a Shanghai police captain.
- The court found that she knew the confidentiality rules and failed to verify the callers before disclosing information.
- UOB said account numbers were not disclosed and its systems remained secure. It contacted affected customers, disabled digital access and helped reset credentials.
- Sentencing is scheduled for December 2025. Penalties can include fines and imprisonment.
- Independent verification, protected credentials, transaction alerts and prompt reporting are key safeguards against impersonation scams.