Three draft standards begin a national security transition
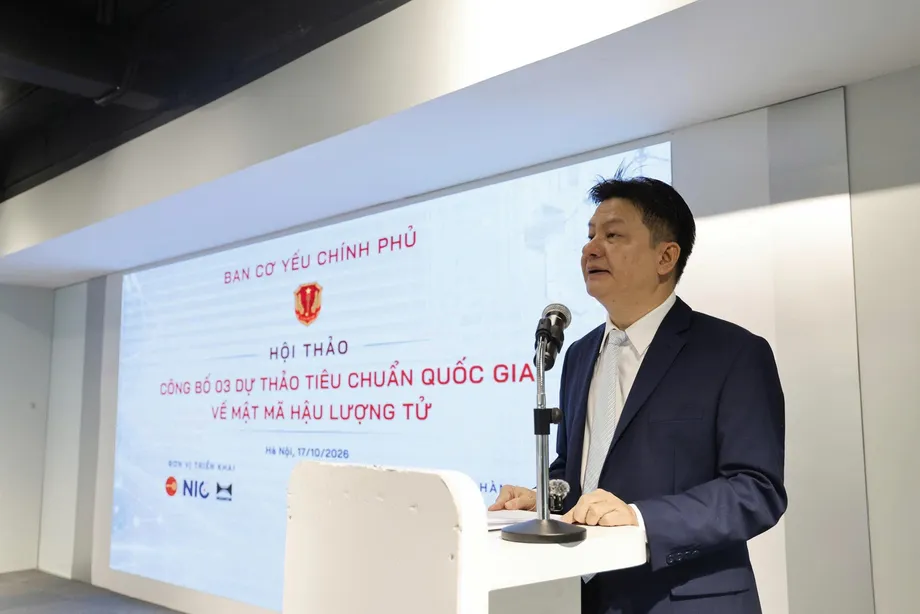
Vietnam's Government Cipher Committee has unveiled three draft national standards for post-quantum cryptography, setting out technical building blocks for a plan to move all information systems important to national security to quantum resistant protection by 2035. Announced in Hanoi on October 17, 2026, the drafts cover the Vietnamese digital signature algorithm HB-PQSign, the key encapsulation mechanism ML-KEM, and the digital signature algorithm ML-DSA.
Contents
- Three draft standards begin a national security transition
- Why encrypted information faces a risk today
- What the three drafts would standardise
- A timetable running from 2027 to 2035
- How hybrid protection would support continuity
- Vietnam wants control across four technical layers
- From mathematical designs to working products
- Specialist shortages could slow deployment
- Public scrutiny will shape the final standards
- Key Points
The committee has opened the specifications and technical explanations to scrutiny from scientists, cryptography specialists and technology businesses in Vietnam and abroad. The drafts concern civilian cryptography, while the broader transition programme addresses the protection of critical national information systems.
Major General Ho Van Huong, deputy head of the Government Cipher Committee, identified a threat that makes preparations urgent: attackers can collect encrypted information today and keep it until more powerful quantum computers become capable of unlocking it. Information that must remain secret for many years is especially exposed to this strategy.
Vietnam's response combines domestic algorithm development, adoption of international standards, public technical review and a staged migration. Existing systems would first be reviewed for risks, with gradual integration of post-quantum cryptography beginning in 2028 and a hybrid transition milestone in 2030.
The practical challenge extends beyond choosing new mathematics. Agencies and businesses will need software, equipment, testing and trained specialists that can support new cryptographic methods while keeping services running. The committee's timetable therefore connects standards development with deployment, rather than treating publication of an algorithm as the end of the work.
Why encrypted information faces a risk today
Ho Van Huong warned that sufficiently powerful quantum computers could break widely used public key cryptographic methods, including RSA and elliptic curve cryptography, known as ECC. These methods help digital systems establish secure connections and verify identities without first sharing a secret through a separate channel.
Quantum computers use different computational techniques from conventional computers. Shor's algorithm, designed for quantum computation, threatens the mathematical problems underlying RSA and ECC. Post-quantum cryptography, or PQC, uses different mathematical foundations intended to resist attacks from both conventional and quantum computers.
The immediate concern is often described as collecting now and decrypting later. An attacker can save encrypted communications without being able to read them, then attempt to recover their contents when stronger tools become available. A document requiring secrecy for decades therefore needs protection that lasts beyond the capabilities of today's computers.
Lieutenant General Dang Vu Son, a former head of the Government Cipher Committee, identified information kept for long periods, digital signatures used in public administration, and financial and banking transactions as areas requiring attention. Confidentiality and signatures serve different purposes: encryption protects the contents of information, while a digital signature helps establish who signed it and whether it has changed.
What the three drafts would standardise
HB-PQSign is a digital signature scheme based on hash functions, mathematical tools that turn data into a digital fingerprint. The draft covers a modified version of an algorithm developed in Vietnam. Its design selectively draws on the SPHINCS+ framework, associated with the international signature standard FIPS 205, while giving Vietnamese researchers control over parameters and operating choices.
ML-KEM performs a different job. A key encapsulation mechanism helps two parties establish a shared secret over a public network. That secret can then support encryption of their communications. Vietnam's draft references ISO/IEC 18033-2:2006/Amd.2:2026.
ML-DSA is a digital signature algorithm based on mathematical structures called lattices. Its draft draws on FIPS 204. In simple terms, lattice cryptography builds security around mathematical problems involving structured collections of points that are intended to be difficult for attackers to solve.
The three drafts therefore address both trust in signed information and the establishment of secrets used to protect communications. Their international references also give Vietnamese developers common technical foundations for building systems that can work with products and services developed elsewhere.
A timetable running from 2027 to 2035
The committee's programme follows two government schemes: development of a quantum resistant cryptographic system for 2026 to 2035, and encouragement of wider participation in civilian cryptography research and application development for 2026 to 2030, with an outlook to 2035. The schemes are identified with Prime Ministerial Decisions 125/QD-TTg and 1226/QD-TTg, respectively.
The policy sits within work implementing Politburo Resolution 56-NQ/TW on development of Vietnam's cryptography sector and Resolution 57-NQ/TW on science, technology, innovation and digital transformation. The transition starts with an examination of existing cryptographic systems and their potential risks.
- By 2027: issue the full set of national technical standards for PQC algorithms, products and security equipment.
- From 2028: gradually combine existing cryptographic technologies with PQC.
- By 2030: complete the planned hybrid integration of PQC into information systems important to national security.
- By 2033: issue further national standards covering PQC and quantum key distribution.
- By 2035: complete the transition to quantum resistant cryptography across 100% of information systems important to national security.
The 2030 milestone concerns the hybrid stage, when established and newer methods operate together. The 2035 target covers completion of the wider transition across the designated critical systems. The target population is those systems important to national security, rather than every device or online service in Vietnam.
How hybrid protection would support continuity
Ho Van Huong said the transition must preserve continuity while coordinating changes across organisations. The deputy head of the Government Cipher Committee described the approach in these terms:
Vietnam's transition to quantum-resistant cryptography must be cautious, coordinated and uninterrupted.
The committee's research includes Hybrid ML-KEM, which combines ML-KEM with an established method such as ECC or RSA. Properly designed, this approach aims to retain protection if one component remains secure, allowing the two methods to support each other during migration.
The engineering matters as much as the selection of algorithms. The 2024 KyberSlash vulnerability, cited in technical discussion of the transition, illustrates the risks associated with implementation. An algorithm's security assumptions and the behaviour of the software running it both require examination.
PQC will be the principal technology for widespread deployment. Quantum key distribution, or QKD, will have a selective role on certain critical communications networks. PQC uses cryptographic algorithms that can run on conventional computing equipment; QKD uses quantum physical processes to distribute keys and requires specialised communications infrastructure.
Vietnam wants control across four technical layers
Nguyen Quoc Toan, director of the Institute of Cryptographic Science and Technology, said national capability depends on mastering four connected layers: algorithm design and security proofs; cryptanalysis; secure implementation and hardware production; and standardisation and testing.
Each layer answers a different question. Designers explain why an algorithm should resist attack. Cryptanalysts actively search for ways to break it. Engineers turn the design into software and hardware that protect secrets during operation. Testing and standards establish shared requirements for assessing the resulting products.
The committee says its work includes HB-PQSign, Hybrid ML-KEM, security analysis in the quantum random oracle model, and development and control of cryptographic parameter sets. Parameters are the settings that determine properties such as security level, processing demands and the size of keys or signatures.
The quantum random oracle model, abbreviated QROM, is a mathematical framework for analysing cryptographic security while allowing an attacker to make quantum queries to an idealised hash function. The research described includes techniques such as Fiat-Shamir with Abort and Fujisaki-Okamoto, alongside Compressed Oracle and Measure-and-Reprogram methods.
For Vietnam, the goal is to develop the ability to inspect, adapt and maintain cryptographic systems domestically. Toan's argument links that capability to control over sensitive information and reduced dependence on outside technical decisions.
From mathematical designs to working products
HB-PQSign's development work includes a reference implementation, test vectors and protections against attacks through unintended information leakage. A reference implementation provides a working model of the algorithm; test vectors supply known inputs and expected outputs so developers can check whether their own software behaves correctly.
Potential applications include digital signatures for government work and centralised signing systems using hardware security modules, or HSMs. These are specialised devices designed to protect cryptographic keys and perform sensitive operations without exposing those keys to ordinary software.
Implementation security requires attention to side channel attacks, in which an attacker studies clues such as timing or power consumption, and fault attacks, which deliberately disrupt a device's operation. These risks help explain why secure hardware and independent evaluation are part of the proposed capability framework.
MK Group representative Nguyen Quoc Han said the company was working with the Institute of Cryptographic Science and Technology to integrate post-quantum algorithms into its MK Lotus operating system. The work is directed towards products supporting areas such as financial transactions, electronic contracts, electronic identity and online public services.
Larger keys and signatures can also place extra demands on networks, storage and devices with limited resources. Public key infrastructure, or PKI, the system of certificates and trusted authorities used to verify digital identities, will need to accommodate those changes. Deployment testing must therefore examine processing speed, compatibility and resource use alongside security.
Specialist shortages could slow deployment
Nguyen Quoc Toan identified four broad challenges: demanding scientific knowledge, the need for cryptographic agility, the gap between theory and deployment, and a shortage of highly trained people. Cryptographic agility means being able to replace algorithms or change their settings when new weaknesses emerge, without rebuilding an entire service.
That flexibility must extend across software, devices and communications protocols. A change made by one organisation can affect the systems it connects to, making coordinated testing necessary if public services and business transactions are to continue uninterrupted.
Toan proposed forming core expert groups around the four capability layers, connecting doctoral training to national cryptography projects, and sending young researchers to leading international centres. He also called for recruitment, pay and working conditions suited to attracting and retaining specialists.
Dang Vu Son said qualified cryptographers would be central to turning the drafts into practical systems. He called for coordination among regulators, research institutes, universities and businesses. Training an independent algorithm designer takes years, while competition for such skills from private companies and overseas employers is already strong.
Public scrutiny will shape the final standards
The Government Cipher Committee has published technical material through the portals of the committee, the Ministry of National Defence and the National Commission for Standards, Metrology and Quality. It also launched a dedicated website to gather feedback from scientists, specialists and technology businesses. No consultation closing date was announced in the workshop details.
Tran Duy Lai and Tran Van Truong, both former directors of the Institute of Cryptographic Science and Technology, proposed wider publication of detailed technical explanations, focused technical discussions and English editions. Those steps would make it easier for international cryptanalysts to examine the designs and contribute detailed assessments.
Vo Xuan Hoai, deputy director of the National Innovation Centre, said the standards would provide a technical basis for evaluating, selecting, testing and deploying security solutions suitable for Vietnam. He called for coordinated work on standards and migration planning, research and trials, and connections between research institutions, universities and businesses.
The centre plans to work with the committee and the institute to connect practical demand with research capability and international expert networks. The next formal milestone is the national standards package due by 2027, followed by gradual hybrid deployment from 2028. Public review, product testing and specialist training now have to turn the three drafts into tools that organisations can operate reliably.
Key Points
- Vietnam announced draft standards for HB-PQSign, ML-KEM and ML-DSA in Hanoi on October 17, 2026.
- The drafts are open to technical review by domestic and international specialists.
- National standards are due by 2027, with gradual hybrid deployment beginning in 2028 and a critical systems milestone in 2030.
- The government aims to transition all information systems important to national security to quantum resistant cryptography by 2035.
- PQC will support widespread adoption, while QKD will be used selectively on critical communications networks.
- Secure implementation, product compatibility and specialist training are central challenges.